Trucking is all about connections. Connections between shippers, brokers, truckers, and receivers. Connections between truck and trailer via brake controllers, power connections, and air hoses. Connections between a truck’s engine, the electronic logging device (ELD), the driver, and inspectors.
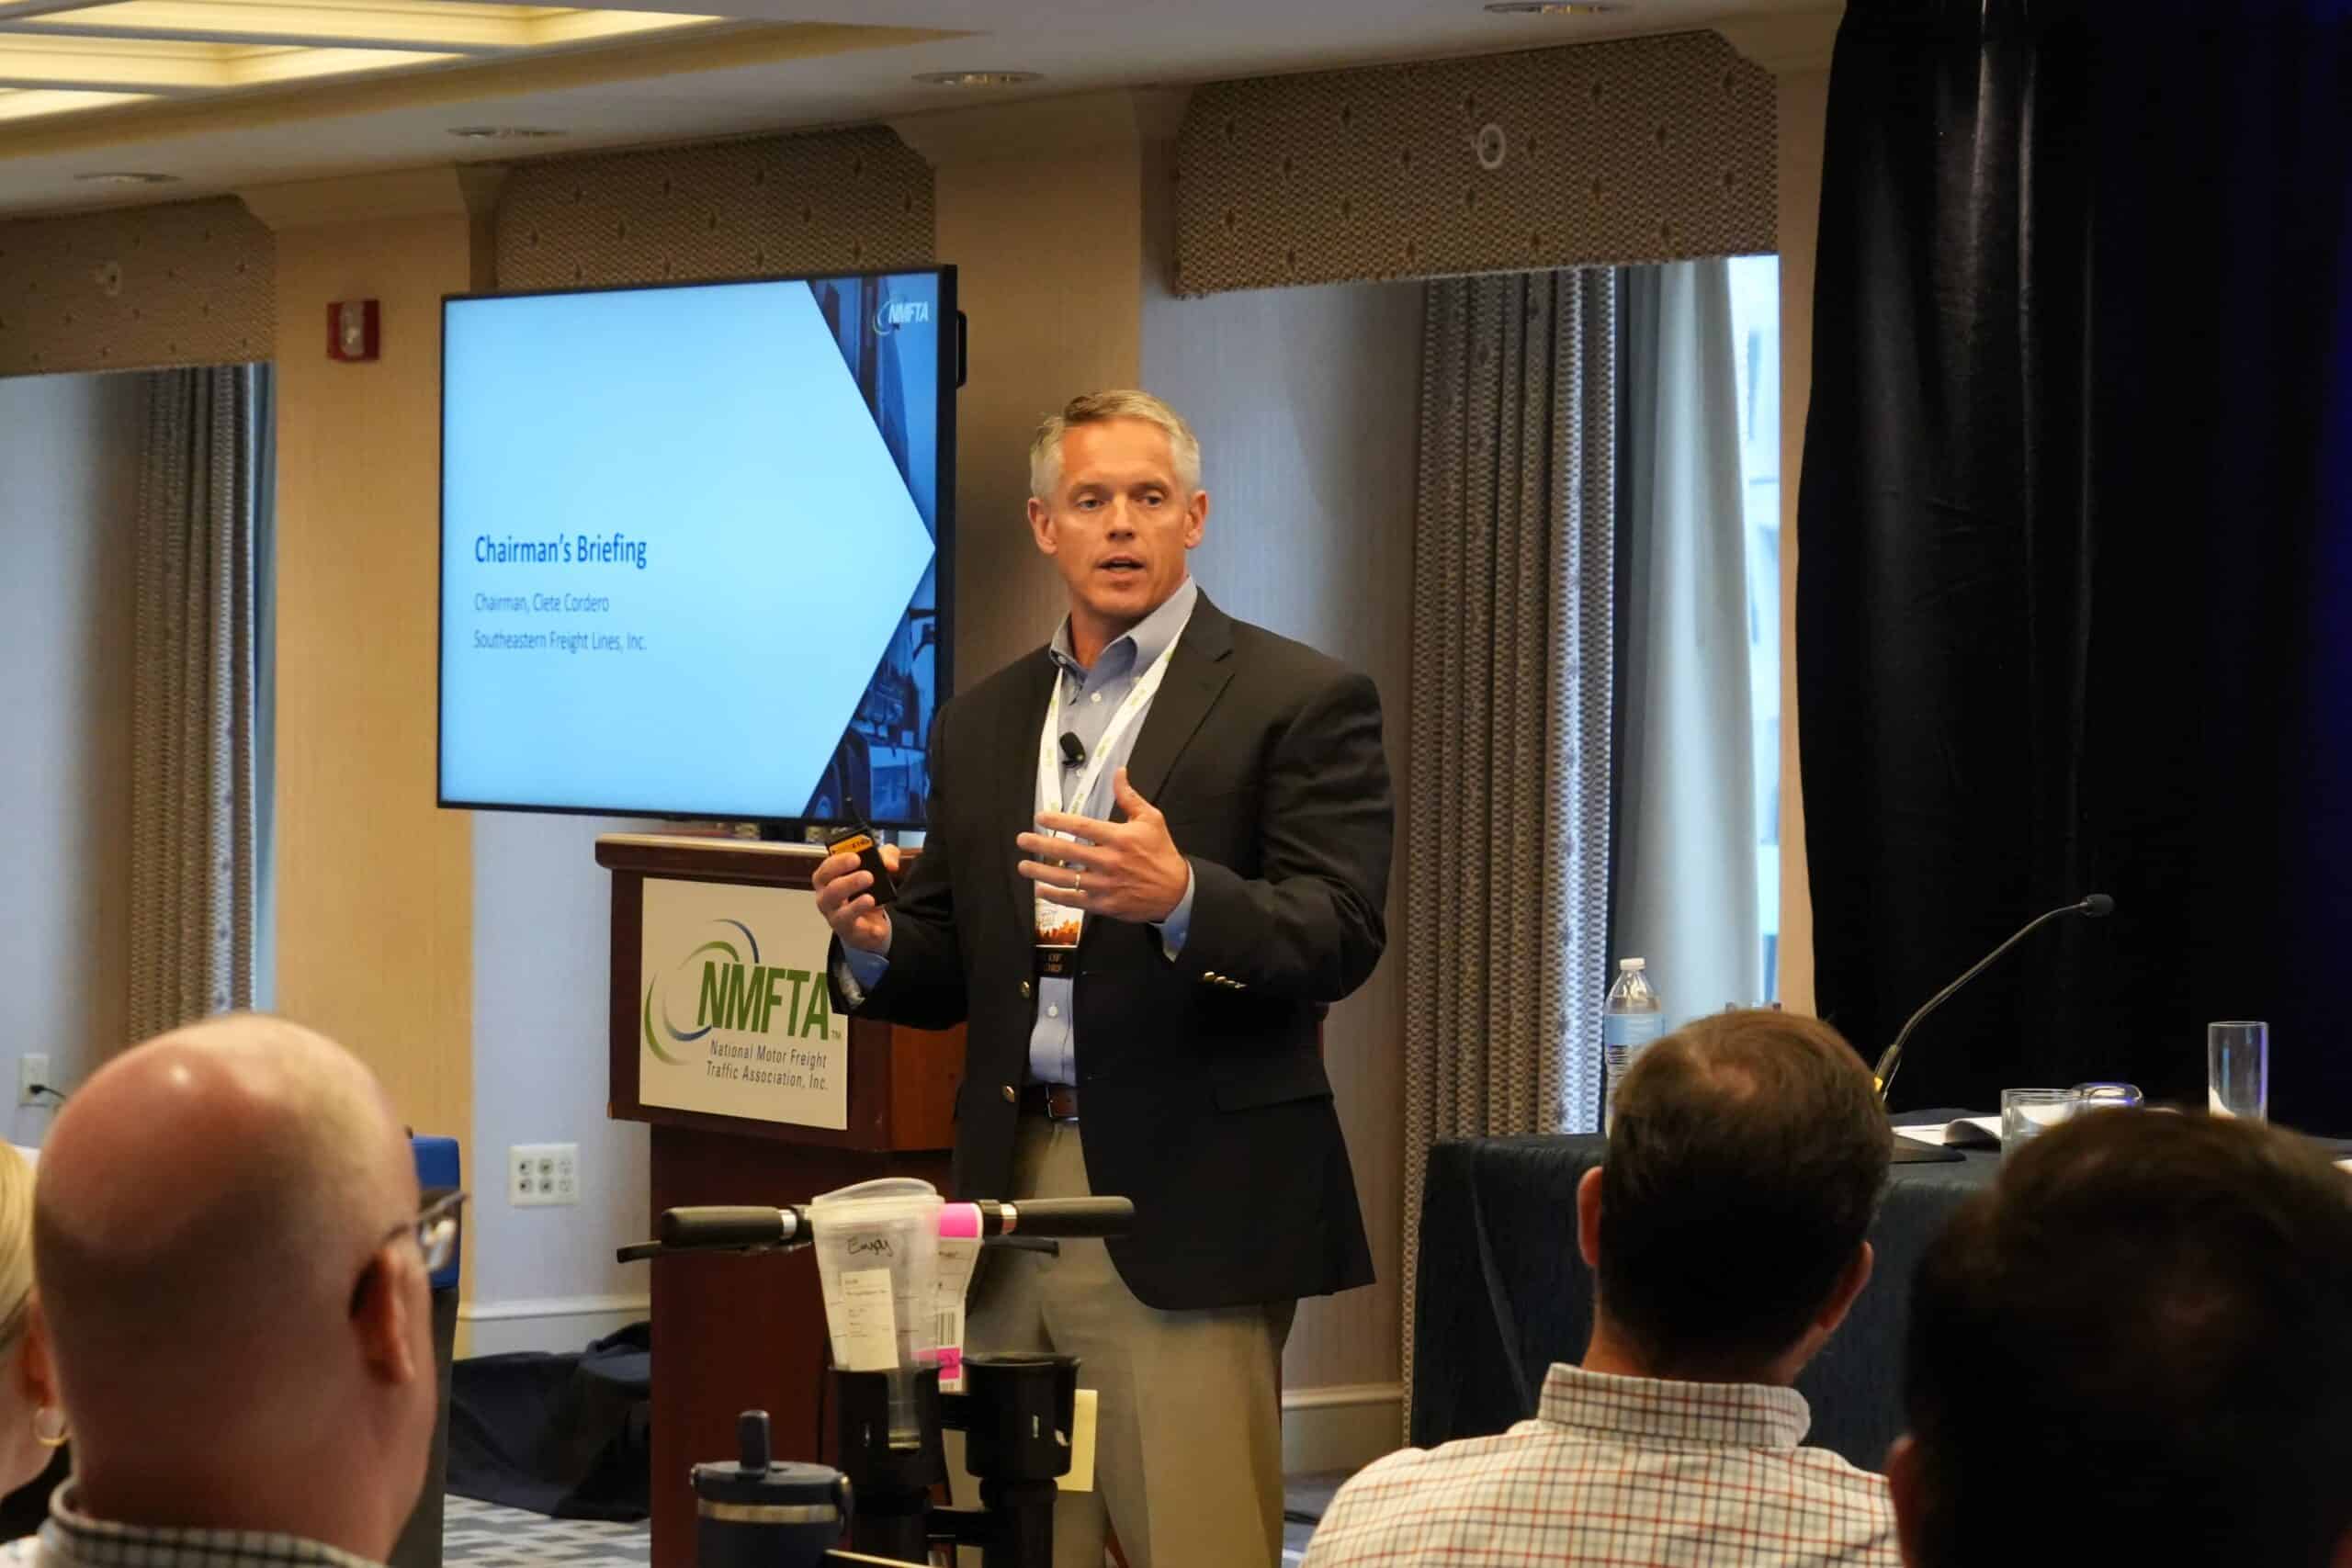
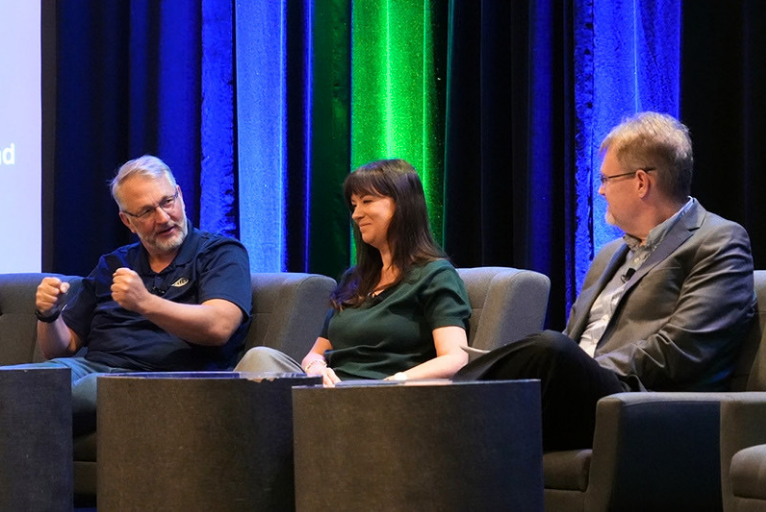
At the NMFTA 2026 Cybersecurity Conference, another kind of connection took center stage: the personal ones between motor carriers, cybersecurity researchers, vendors, insurers, podcasters, and NMFTA itself. As Ken Heskett, cybersecurity research engineer for NMFTA put it, those connections “will help the trucking industry fend off cybersecurity bad actors and present strong and unified messages to regulators” to reform outdated regulations, update technology, and reinforce law enforcement’s fight against cargo crime.
Broad Coverage, Deep Dives
The agenda ranged widely as some sessions covered broadly applicable topics like incident management, frameworks for cybersecurity program design, and how bad actors misuse new technologies for fraud. Others were deep technical dives into white-labeled ELDs and maintenance updates that disguise security patches. While others focused on using threat intelligence to detect when the industry is targeted for social engineering and phishing.
For Anne Zachos, cybersecurity research engineer for NMFTA, the asset-focused technical track stood out. “This year’s conference was great as always. I always enjoy meeting people in the industry and the fresh perspectives they bring, as well as catching up with returning attendees,” she said. “The technical track this year was packed with excellent content.”
The Future of ELD Certification
Device trust was a recurring thread. “The conference was a great opportunity to learn and collaborate,” said Joe Ohr, chief operations and technical officer for NMFTA, “We discussed the future of ELD certification with FMCSA and also focused on white-labeled ‘Chameleon ELDs’ and why it is a challenge for the industry and FMCSA certification.”
TCAT Hands-On Session
One highlight was the TCAT training session, where attendees had the opportunity to move from theory to practice. “We had really good engagement, especially with our TCAT training session,” Zachos said. “It was wonderful to see people be able to actually get hands on and try using real life trucking cybersecurity tools.”
Ben Gardiner, senior cybersecurity engineer for NMFTA who delivered the session, agreed: “It was a pleasure to be a part of yet another one of these. And delivering the TCAT training ‘teaser’ went great. This will be a useful tool for the fleets and we’re looking forward to more beta testers.”
Fleets interested in joining the beta can reach out to the NMFTA cybersecurity team at cyber@nmfta.org.
Compete in Business, Collaborate on Security
This event is the trucking industry’s only cybersecurity conference which makes this gathering even more special. Each year, the conference makes these connections possible through networking events and a clear call for collaboration across every facet of the trucking industry. This year’s conference really drove home the need to pivot from a reactive security stance to a proactive security stance. With AI-powered attacks happening at an unprecedented scale and with ever-increasing speed, this is more important now than ever. So is teamwork; sharing what techniques we’ve used that worked well and lessons learned from things that didn’t go so well. All of this is valuable intelligence for our peers.
Miss this year’s conference? Mark your calendars for September 2027. We look forward to seeing you next year. Subscribe for 2027 updates at nmftacyber.com.